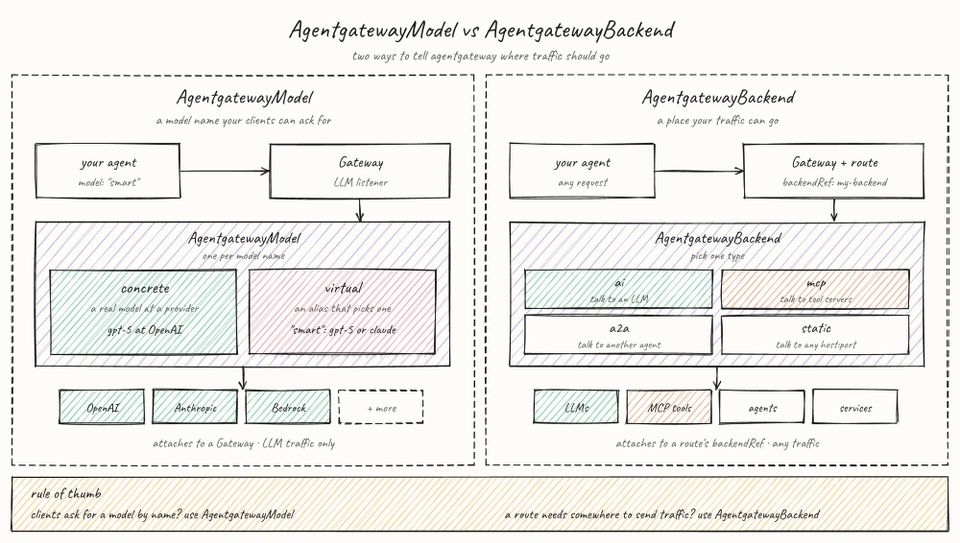
Knowing what LLM you're routing to, whether or not failover for more expensive tasks exists, what LLMs are available, and policy enforcement/implementation for the people accessing LLMs are critical pathways
Many of us are "hands-on-keyboard" interacting with Agents in our terminal or via a desktop app. That's, however, when you want to do something at the exact
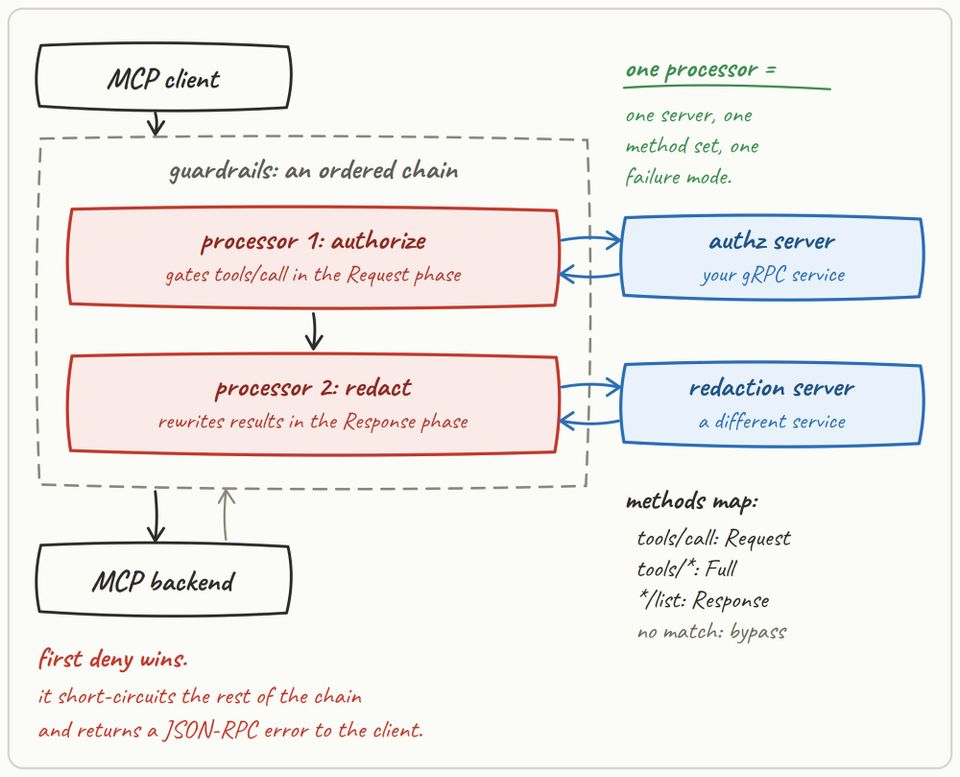
A typical gateway comes with a lot of policy enforcement, authentication/authorization implementations, and filtering for both agentic and API-centric traffic. However, there may come a time when you need:
* Custom auth,
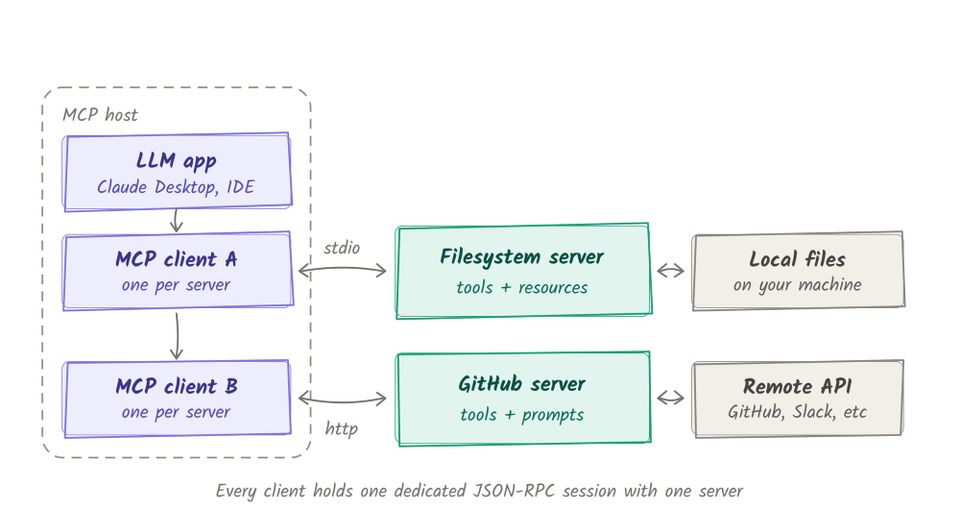
The MCP protocol can now be stateful or stateless, ingest only one tool to the Agent, call API endpoints, and use functions/methods in a codebase as tools. The one concern still, however,
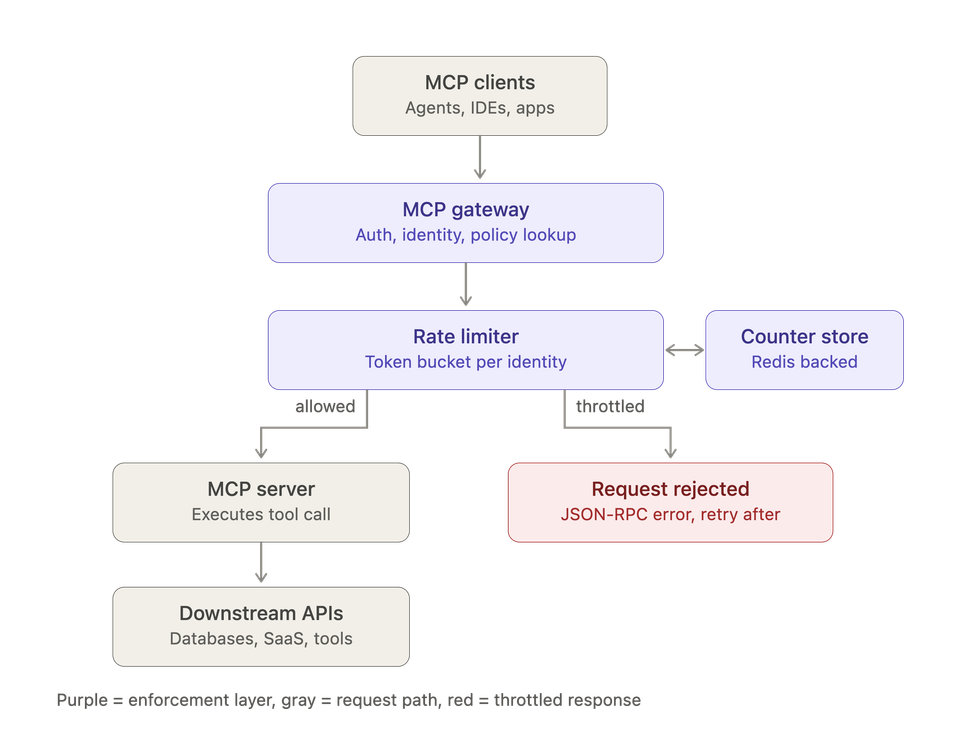
Without proper controls for how many times an Agent/LLM can hit an MCP Server, you open yourself up to potential DOS attacks, memory hogging, insane API bills, and server/system overload. Luckily,